Information security is more than technology — it requires effective governance, risk management, and continuous improvement.
ISO/IEC 27001:2022 is the updated international standard for Information Security Management Systems (ISMS). It helps organizations systematically manage information security risks and protect the confidentiality, integrity, and availability of information.
What Changed?
The 2022 revision introduces important updates to address evolving cybersecurity threats and modern technology environments.
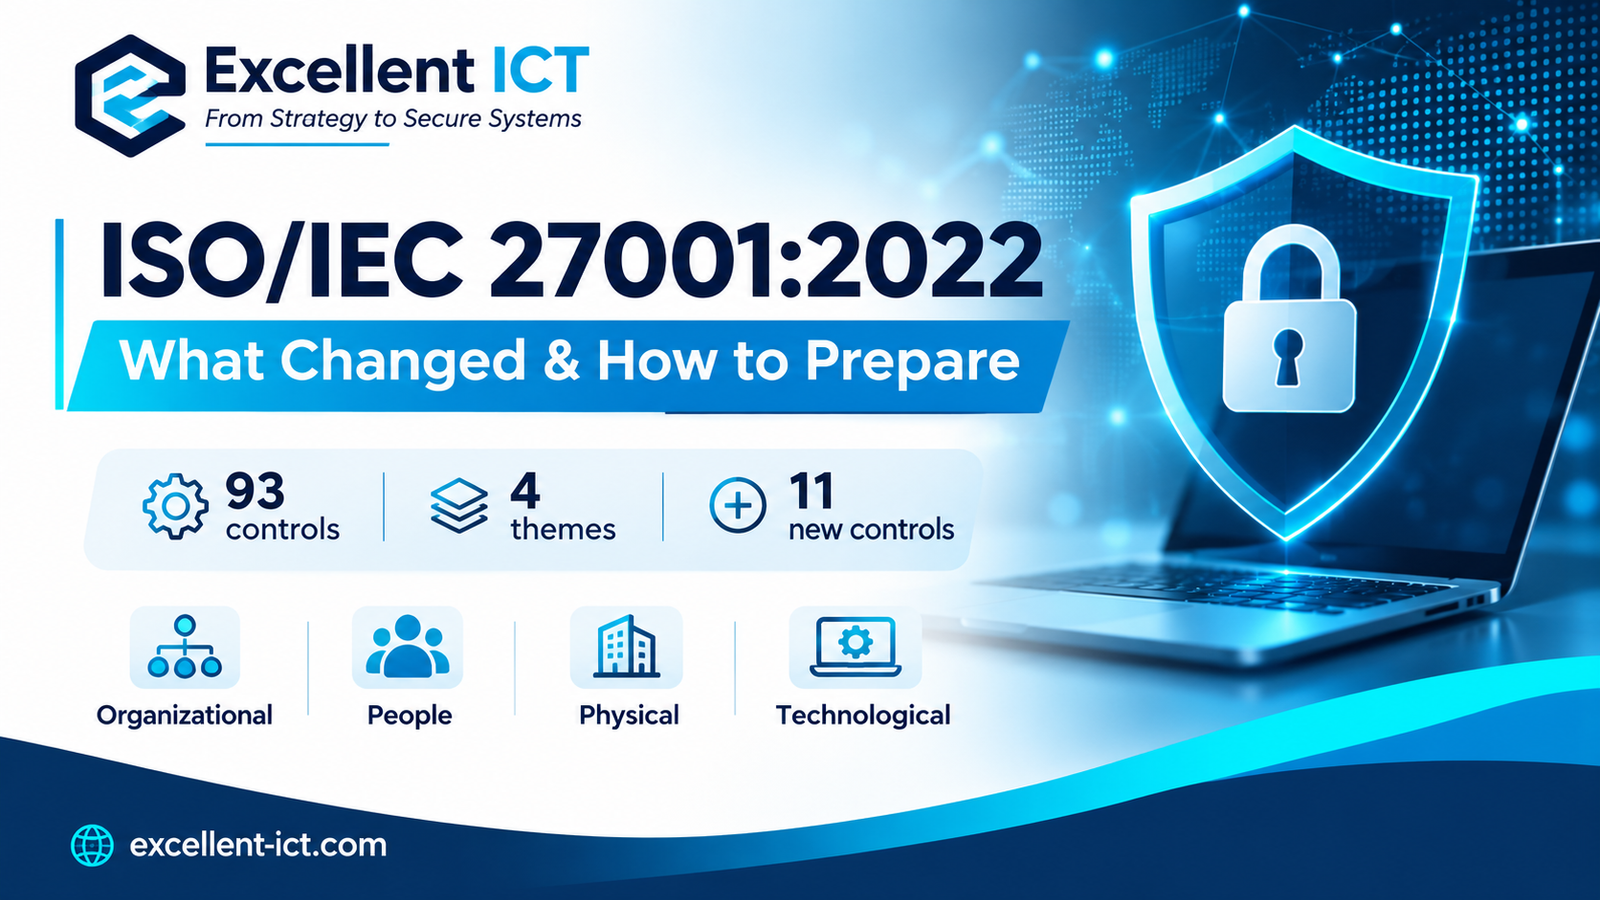
- 93 security controls organized into four categories: Organizational, People, Physical, and Technological, replacing 114 controls across 14 domains.
- 11 new controls, addressing areas such as threat intelligence, cloud security, data leakage prevention, configuration management, and secure coding.
- Updated control structure, making it easier to align security measures with organizational risks and responsibilities.
The core ISMS requirements remain largely unchanged, with the most significant updates affecting Annex A.
How Should Organizations Prepare?
Organizations implementing ISO/IEC 27001:2022 should focus on five key actions:
- Conduct a gap assessment to identify differences between existing practices and the updated standard.
- Review information security risks and update the risk treatment plan.
- Update the Statement of Applicability (SoA) to reflect the revised Annex A controls.
- Implement relevant security improvements and update policies, procedures, and supporting documentation.
- Perform internal audits and management reviews to evaluate ISMS effectiveness and identify opportunities for improvement.
The transition period from ISO/IEC 27001:2013 ended in October 2025. Organizations pursuing certification should now prepare against the 2022 edition.
How Excellent ICT Can Help
Excellent ICT supports organizations through ISO/IEC 27001 gap assessments, ISMS implementation, risk management, documentation, internal auditing, and certification readiness assessments.
Certification audits are conducted by independent, accredited certification bodies.